
Network Topology
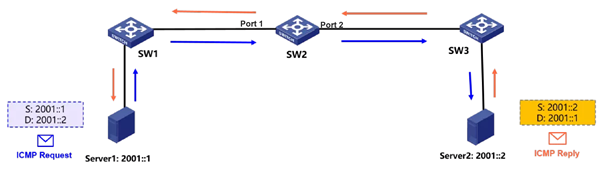
ICMPv6 packet accounting follows the same principle as ICMP packet accounting. The difference is that you must create an IPv6 ACL to match IPv6 packets.
In addition, because IPv6 carries many different types of ICMPv6 messages, the icmp6-type field has to be added when you count IPv6 ping packets, so that the match is precise:
• echo-request or type = 128: the request packet of an IPv6 ping
• echo-reply or type = 129: the reply packet of an IPv6 ping
In the example, the IPv6 ACL matches IPv6 ping request packets with source IP 2001::1/128 and destination IP 2001::2/128.
Configuration Steps
Step 1: Define an IPv6 ACL that matches ICMPv6 traffic in one direction (a Request packet in this example)
acl ipv6 advanced 3000
rule 0 permit icmpv6 source 2001::1/128 destination 2001::2/128 icmp6-type echo-request
Step 2: Define a class that matches the ACL, plus the accounting action
traffic classifier classifier_1
if-match acl ipv6 3000
traffic behavior behavior_1
accounting packet
Step 3: Define a QoS policy that associates the class and the action
qos policy policy_1
classifier classifier_1 behavior behavior_1
Step 4: Apply the QoS policy to the right interface and direction
interface GigabitEthernet 1/0/1
qos apply policy policy_1 inbound
interface GigabitEthernet 1/0/2
qos apply policy policy_1 outbound
Step 5: Reset interface counters and ping through 001::1/128 to 2001::2/128
<H3C>reset counters interface
Step 6: View Traffic Qos results with the command: display qos policy interface inbound/outbound
<H3C>display qos policy interface inbound
Interface: GigabitEthernet1/0/1
Direction: Inbound
Policy: policy_1
Classifier: classifier1
Operator: AND
Rule(s):
lf-match acl ipv6 3000
Behavior: behavior1
Accounting enable:
5 (Packets)
<H3C>display qos policy interface outbound
Interface: GigabitEthernet1/0/2
Direction: Outbound
Policy: policy_1
Classifier: classifier_1
Operator: AND
Rule(s):
if-match acl ipv6 3000
Behavior: behavior1
Accounting enable:
5 (Packets)
Key Configuration
Need to pay attention to where the traffic is going.